API security screen examples
API security screen design examples from SaaS apps. Browse examples from Appwrite, Okta, Parallel.
Explore the examples
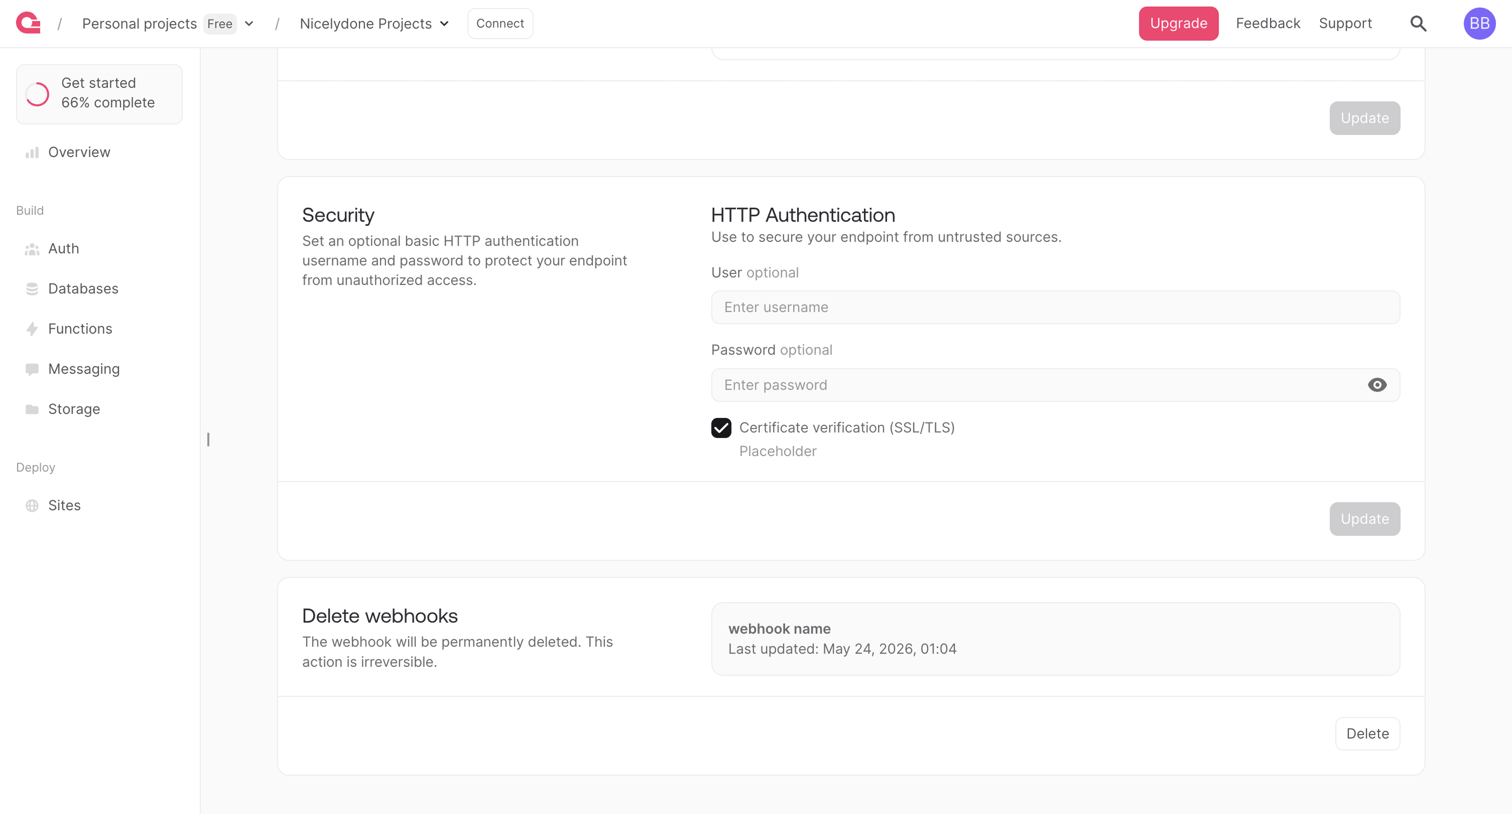
Settings page where the user configures HTTP authentication and certificate verification for a webhook, with an option to delete it.
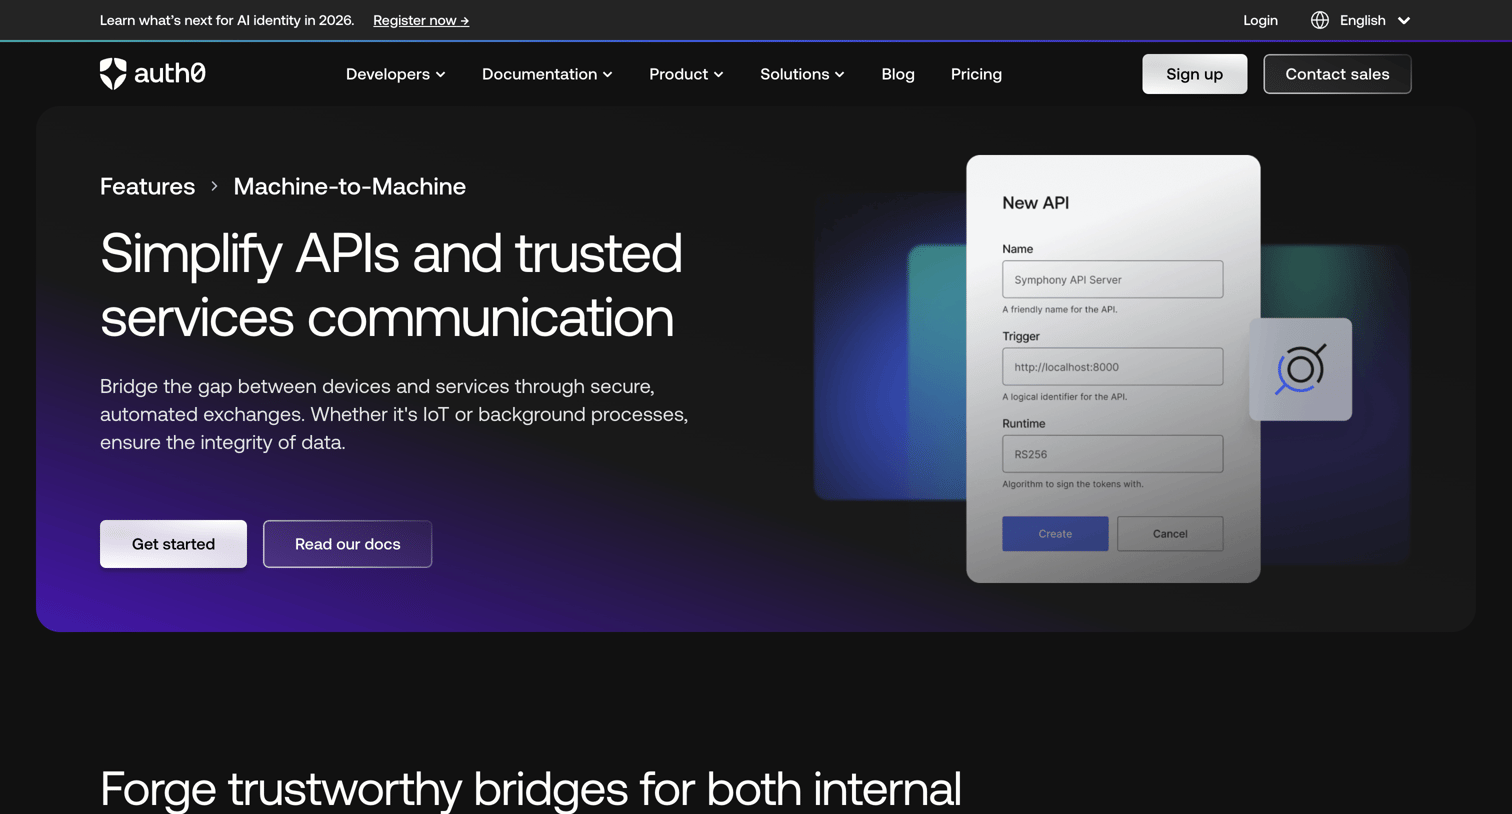
Feature page explaining Auth0's machine-to-machine communication capabilities, highlighting API onboarding, granular permissions, and OAuth2 security standards.
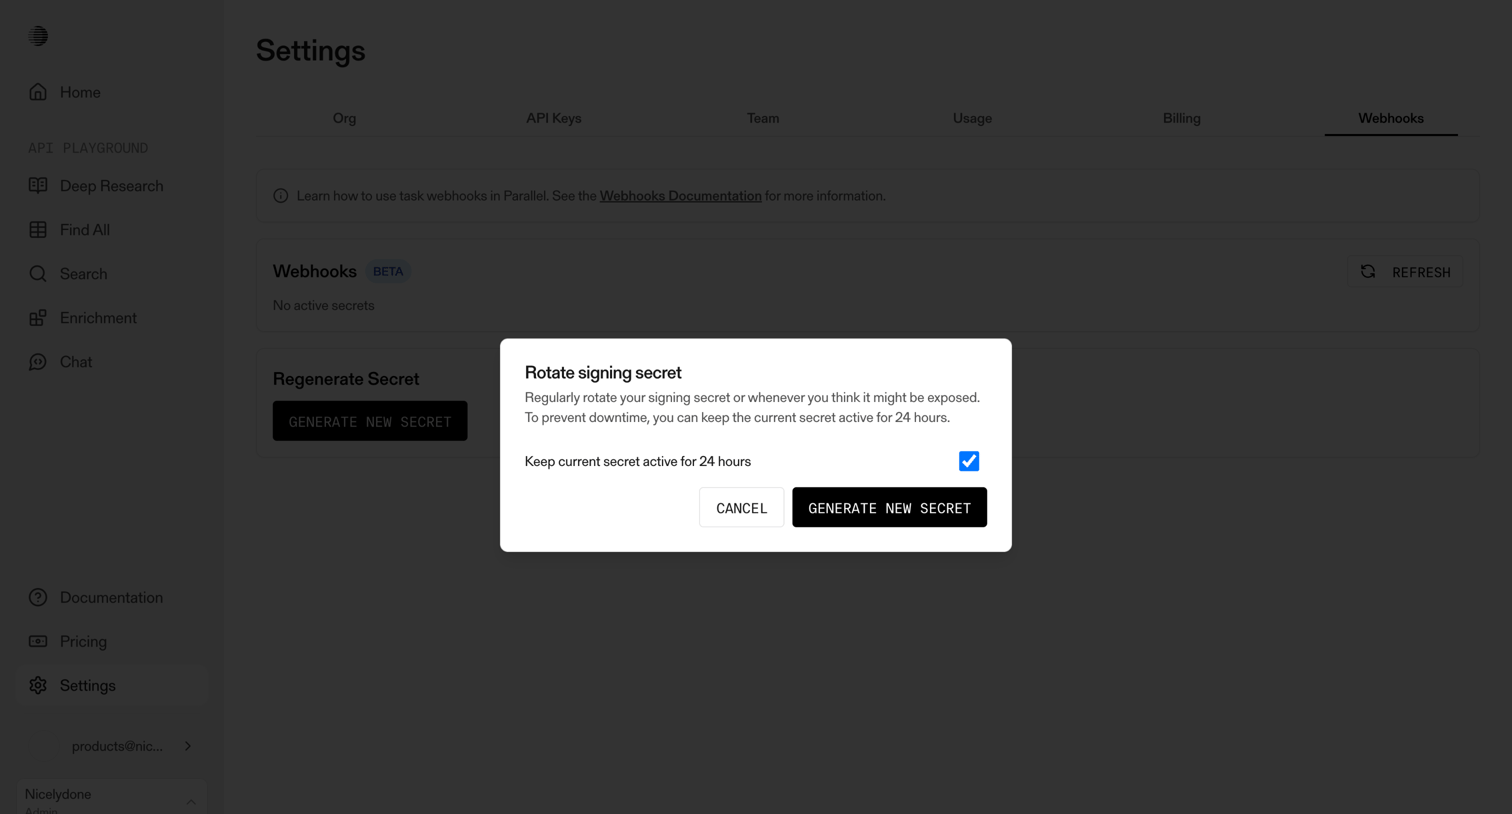
Settings page where the user is prompted to rotate their webhook signing secret via a confirmation modal, with an option to keep the current secret active for 24 hours.
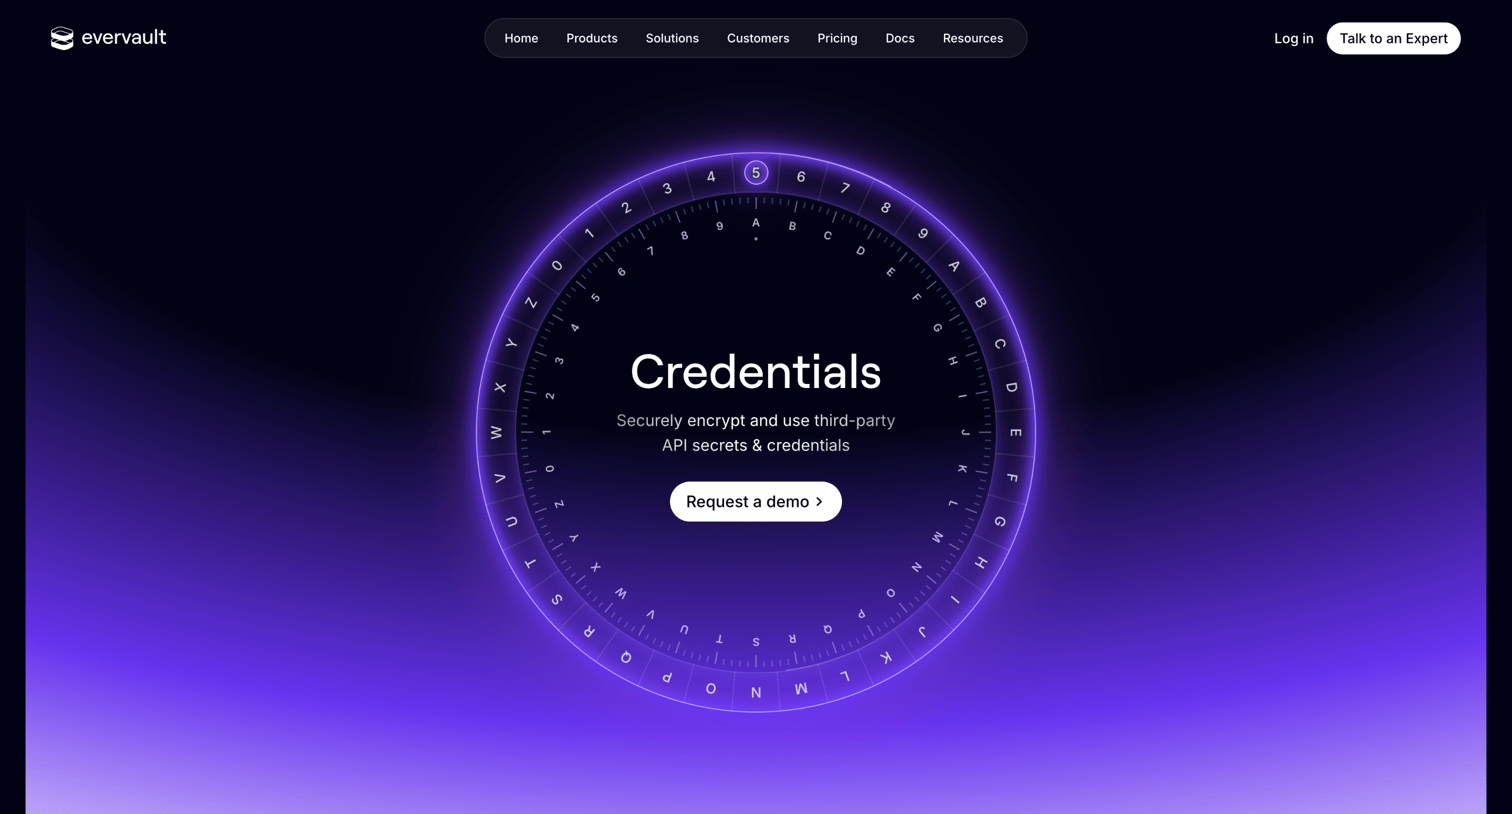
Marketing page for a credentials solution detailing how to securely encrypt, authenticate, and integrate with third-party APIs.
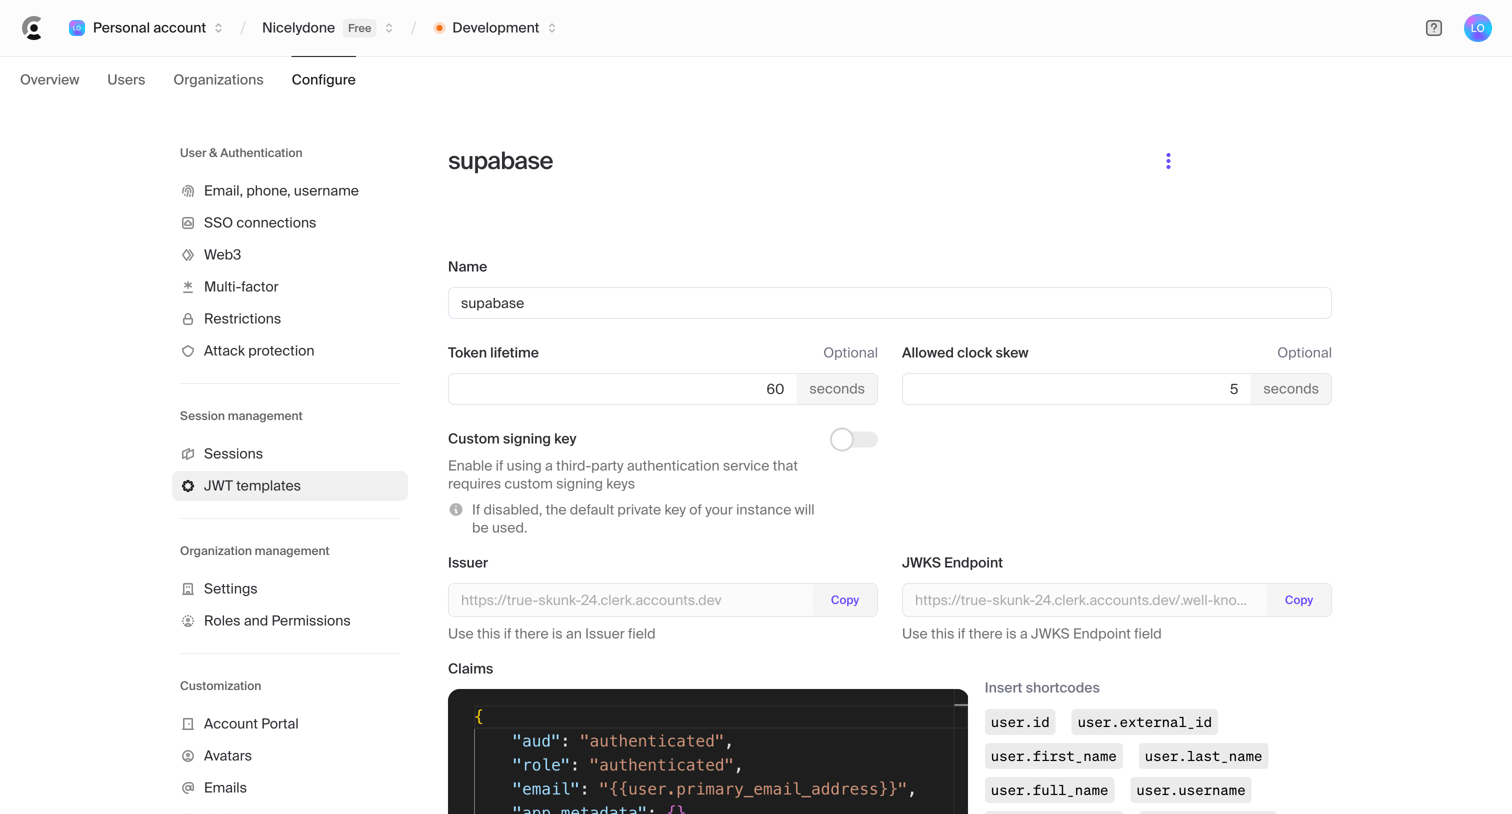
Settings page where the user configures a Supabase JWT template, including token lifetime, custom signing keys, issuer, and claims via a JSON editor.
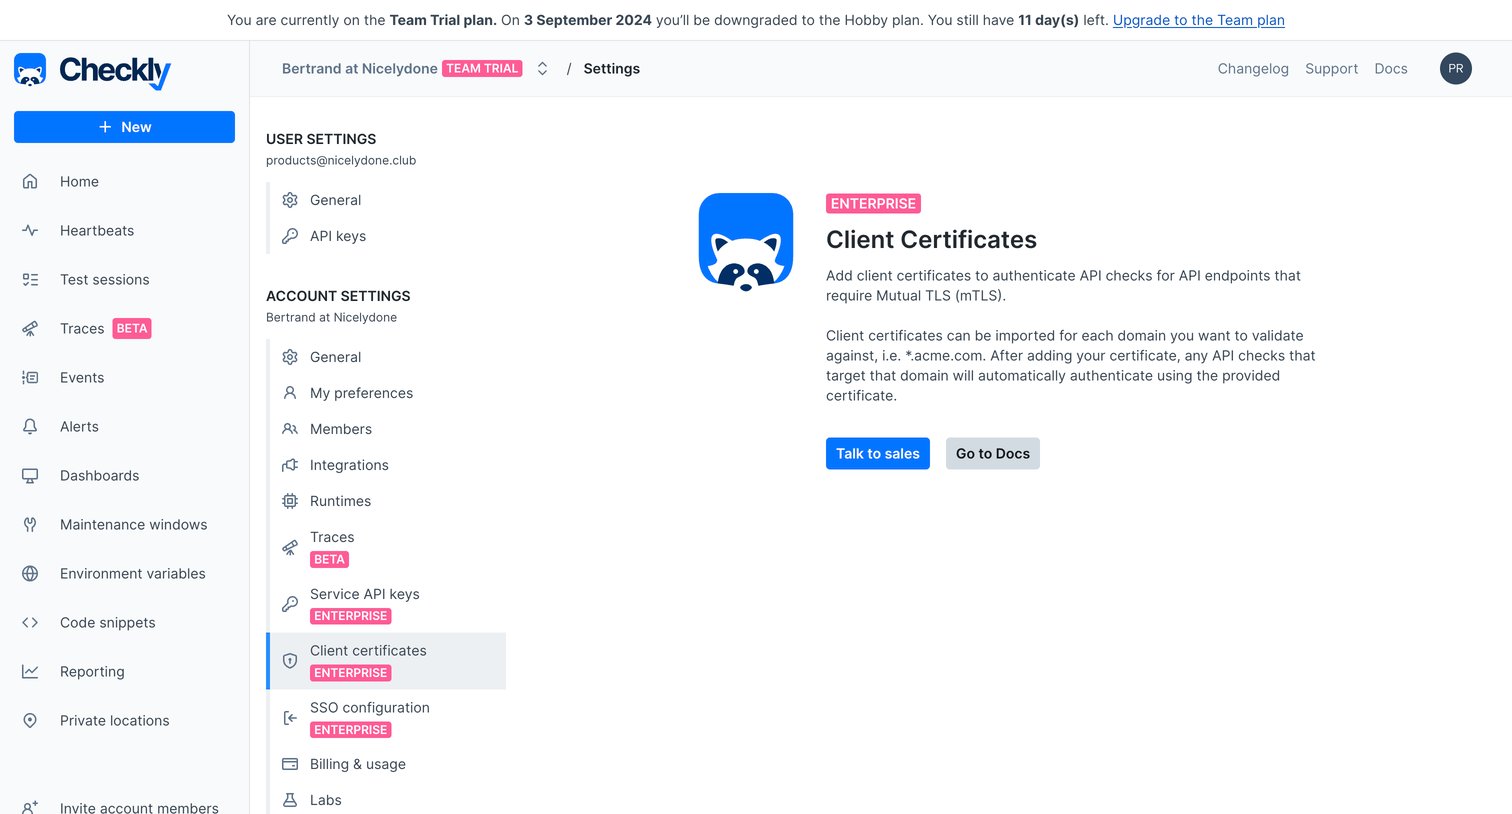
Settings page where the user encounters a feature gate for client certificates and is prompted to contact sales to upgrade to the Enterprise plan.
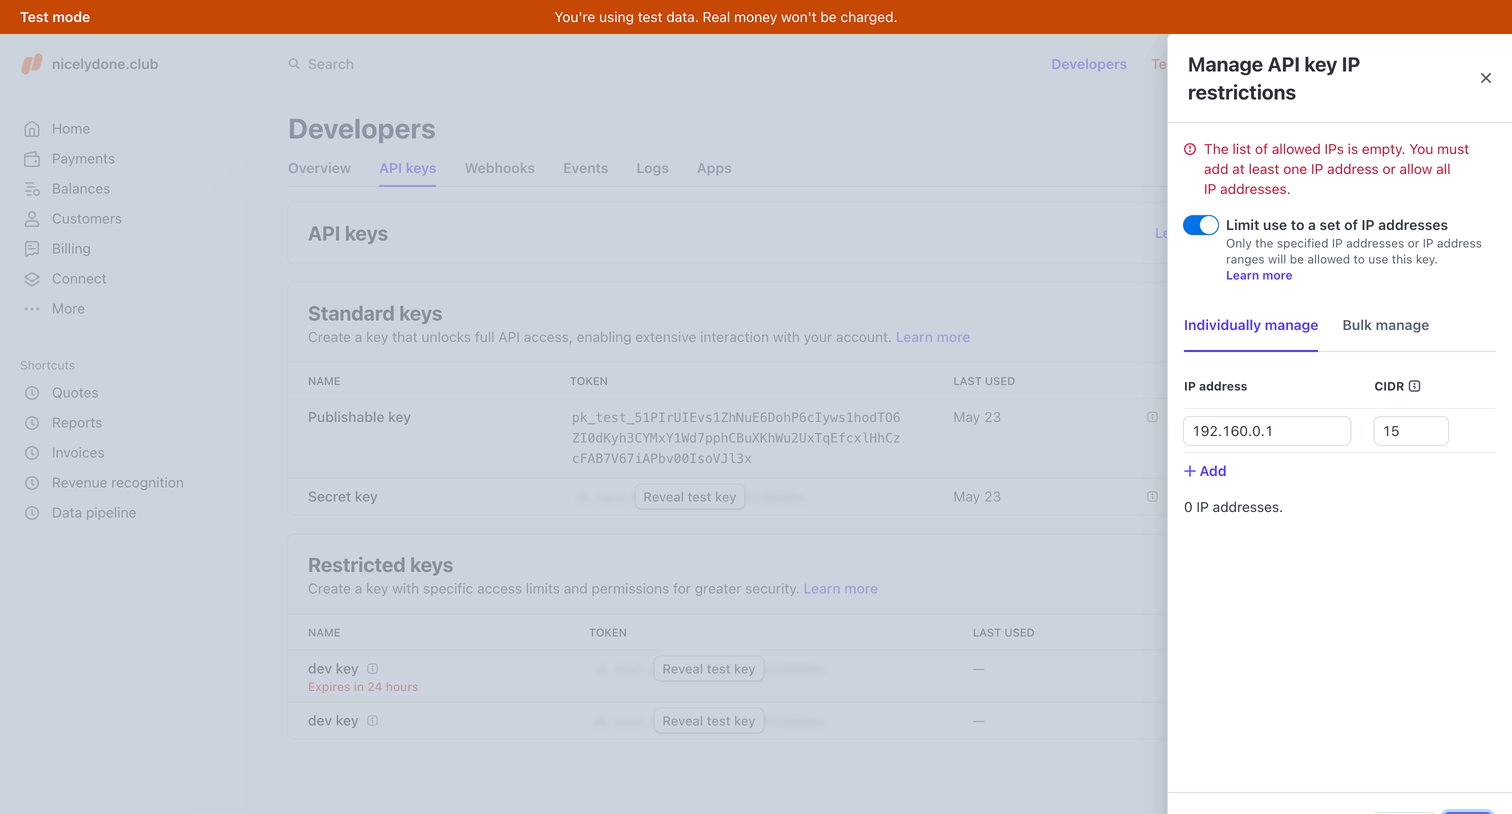
Settings page where the user manages standard and restricted API keys, with a drawer open to configure IP address restrictions.
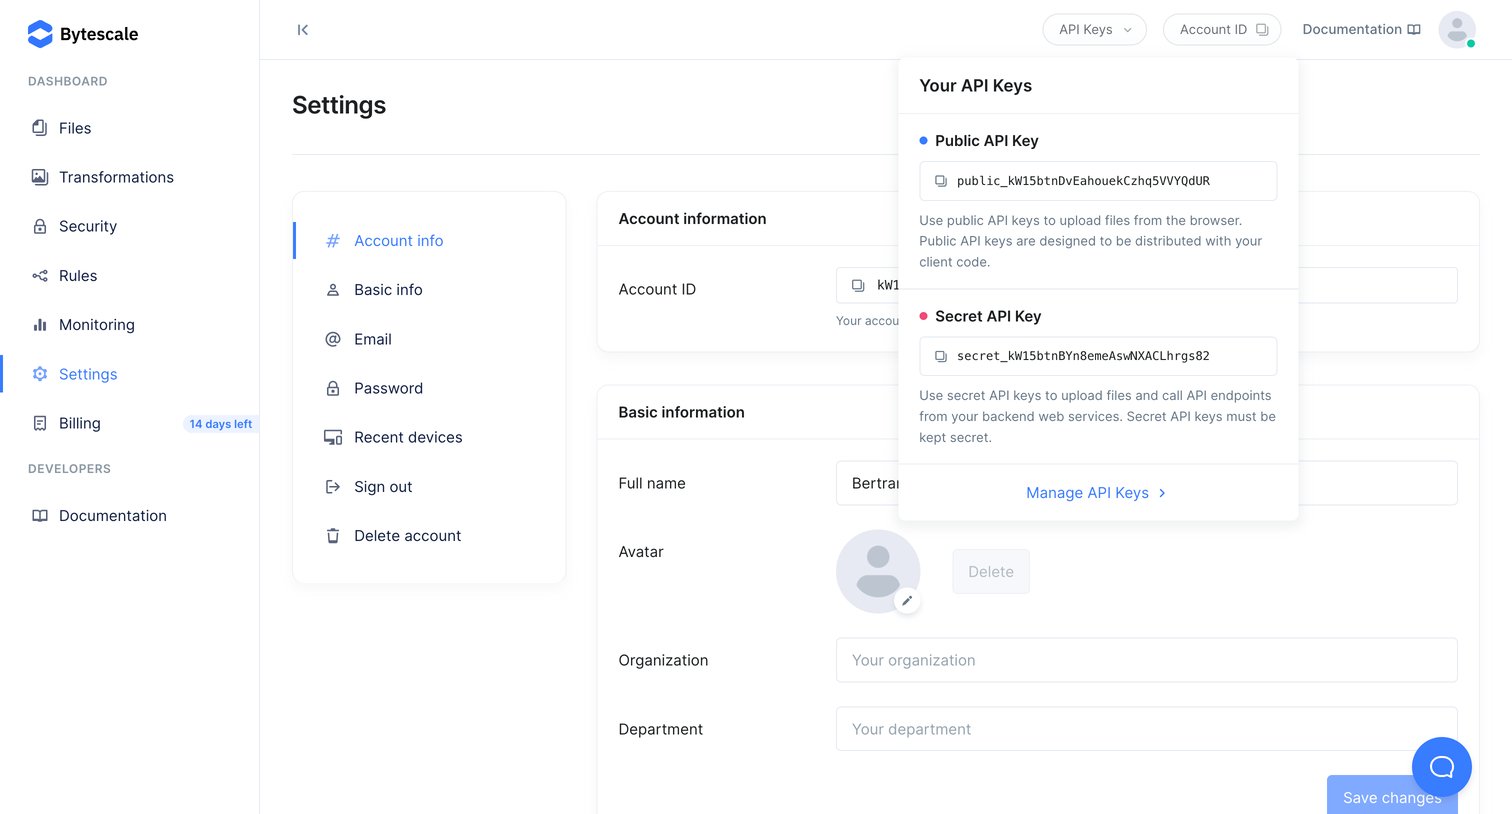
Settings page where the user manages their basic account profile and views active API keys via a top navigation popover.
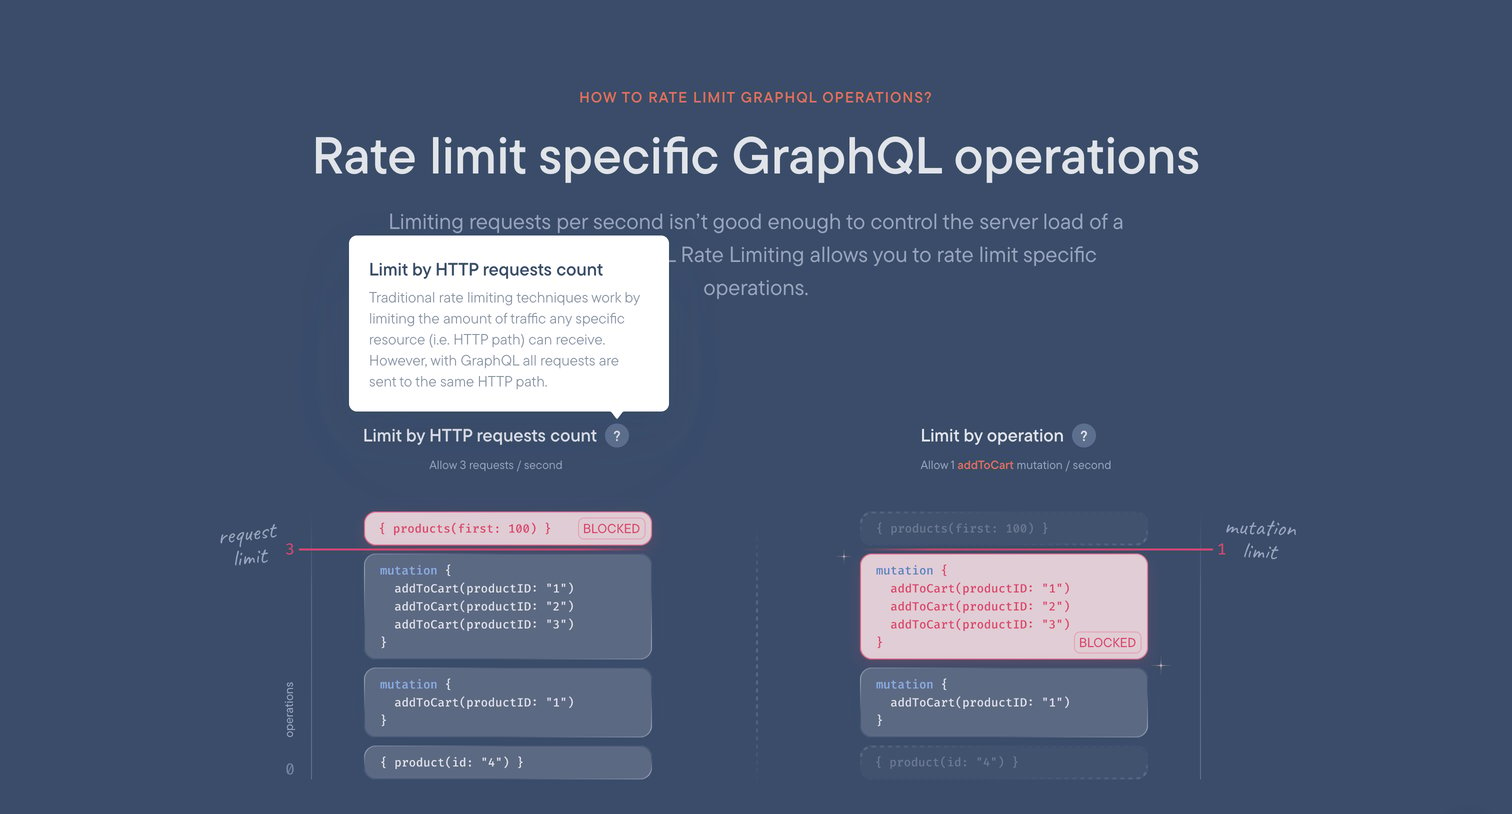
Feature page section explaining GraphQL rate limiting by comparing HTTP request counts versus specific operation limits using visual code stacks.
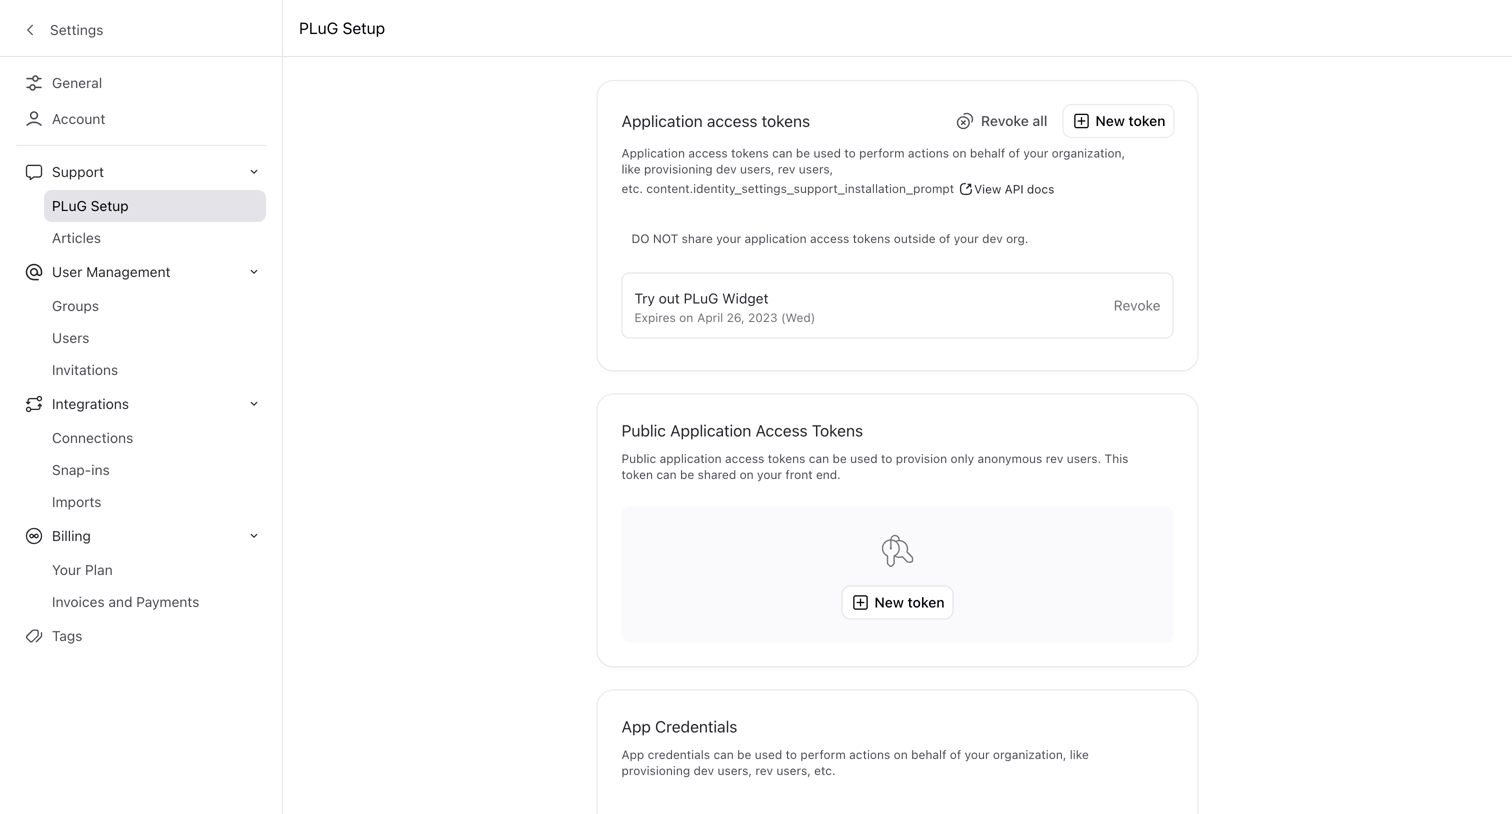

Settings page where the user manages application access tokens and app credentials for their support widget.
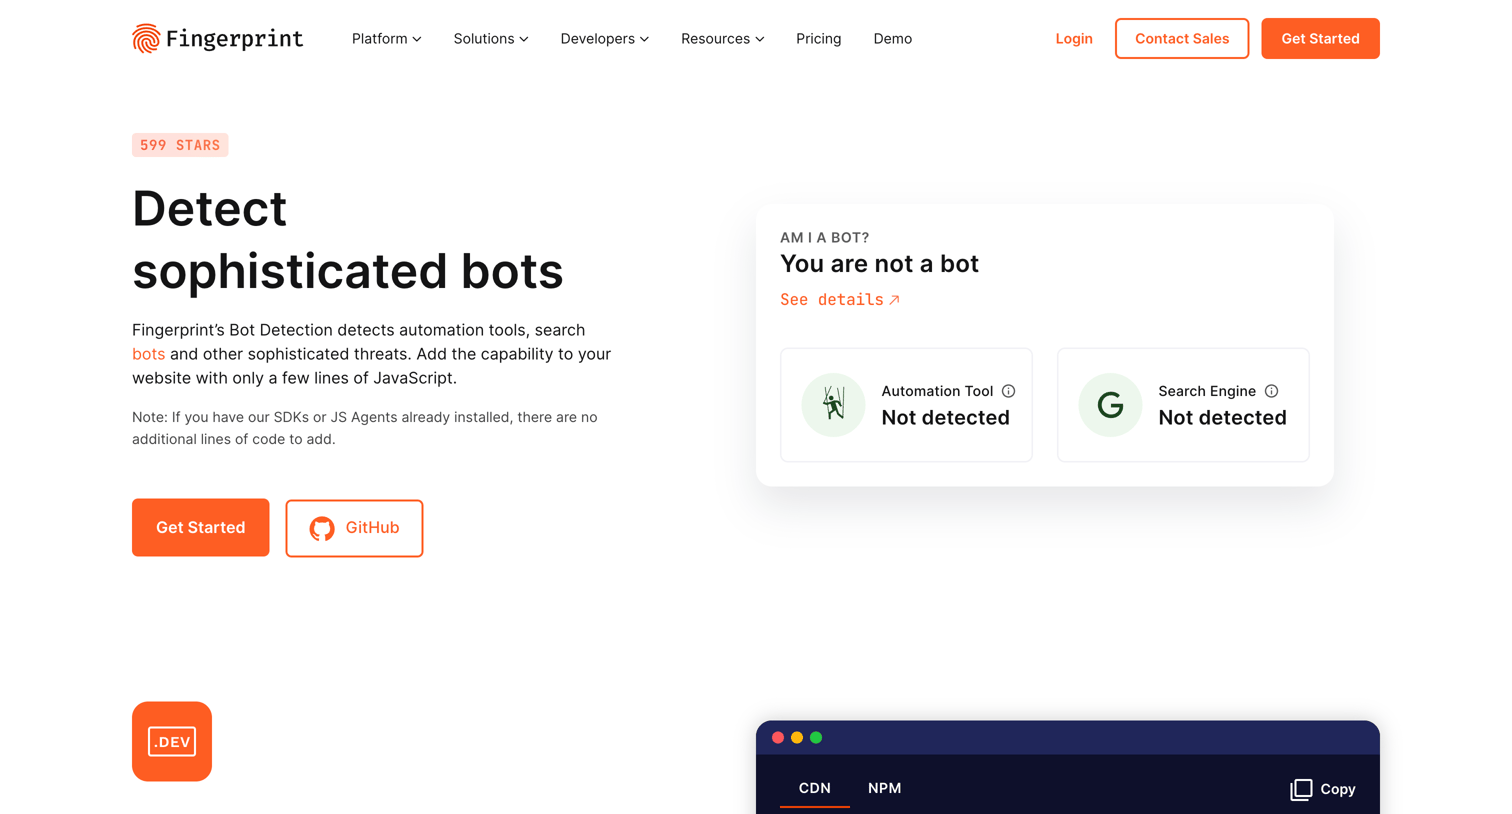
Feature page for a bot detection API detailing developer integration, cloud provider support, and common use cases like preventing fraud and scraping.
Explore the full SaaS screen library
Upgrade to unlock the full library.
Trusted by the best teams


